Available for work

Maliq Barnard — Full-Stack Developer & Security Researcher. I build the systems you will rely on,
and find the vulnerabilities in the ones you already use.

Maliq Barnard — third-year university student and self-taught developer. I build production software and conduct independent security research across Apple, Microsoft, MongoDB, and open source.

Maliq Barnard
Maliq Barnard · Canada, AST/ADT
Security Research
macOS internals, XPC reversing, sandbox escapes. Active across Apple, Microsoft, MongoDB, and HackerOne.
Production Software
Full-stack platforms built and shipped. PHP, Python, React, Swift. Whatever the job needs.
Photography
Editorial landscape work. BC to the Northwest Territories, mostly shot from the side of the road.
Writing
Technical research, opinion pieces, and the occasional essay that has nothing to do with code.

Selected work

Production systems built from the ground up. Self-taught, self-directed, all shipped.

farpsec.xyz
FARPSEC landing page
farpsec.xyz/intelligence
FARPSEC intelligence feed with CVE publications
01
Security Research Vulnerability Discovery

FARPSEC

Security research lab focused on operating system internals and architectural vulnerability discovery. Published CVEs, an Apple security acknowledgement, and an active disclosure pipeline.

IPC surface tracing, memory management auditing, state-aware exploit development. Responsible vendor disclosure throughout.

  • MongoDB Compass: one-click RCE
  • Apple bluetoothd: 0-click overflow
  • CVE-2026-69446: Microsoft Edge & To Do
Independent Research

Finding what scanners miss.

Reverse-engineering OS internals, tracing IPC surfaces, building exploit primitives. Then reporting responsibly. Vulnerabilities confirmed by Apple Security Engineering, CVEs published, patches merged upstream.

Apple Zen Browser Microsoft HackerOne
$ farpsec --recent
10.05 MongoDB Compass · RCE 10.04 Apple bluetoothd · 0-click 10.04 CVE-2026-69446 · Microsoft 08.27 Apple authd · FileVault keys 08.21 NordVPN · IP + GPS at rest $ scope: macOS internals, IPC, crypto, auth
$ tools: LLDB, Ghidra, Python, Frida
$ status: active
02
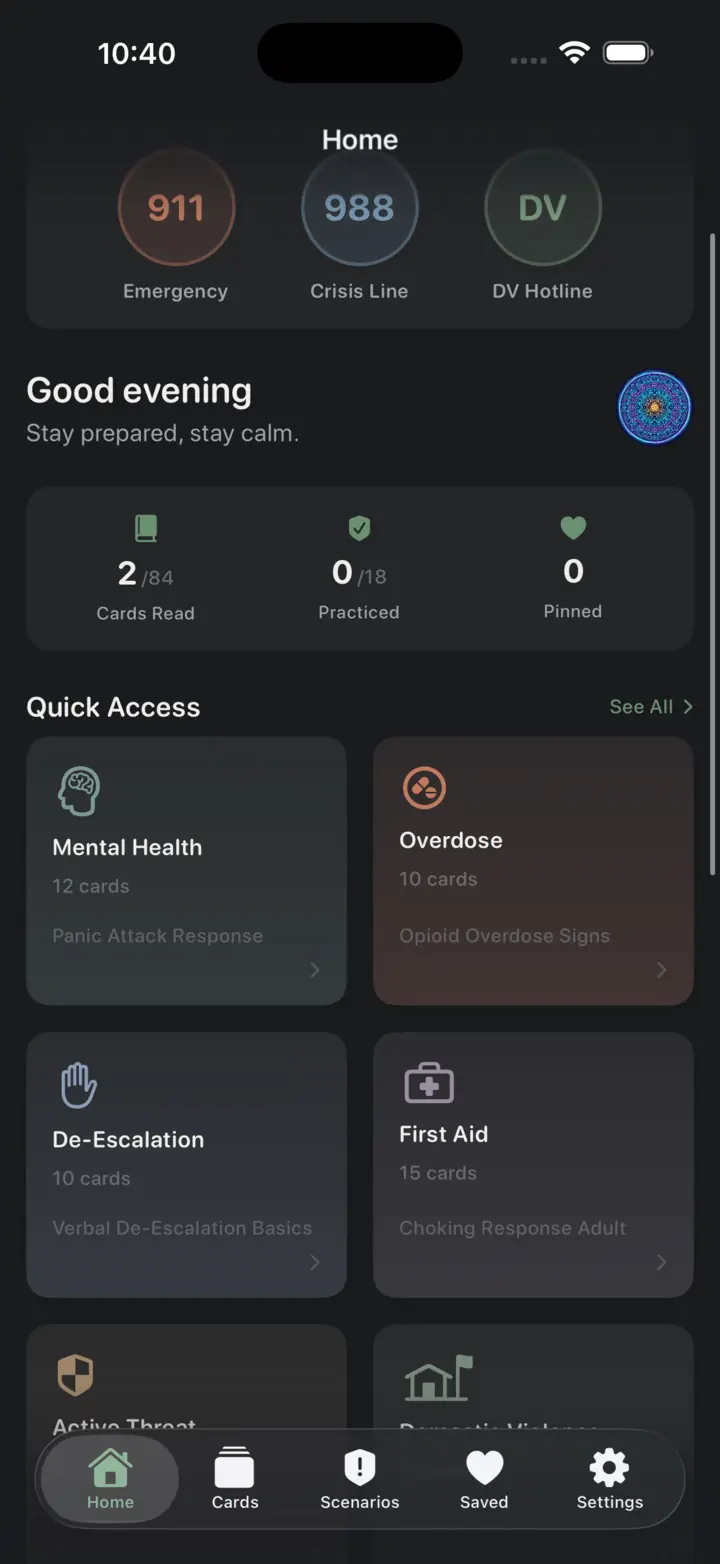
SafeGuard home screen
SafeGuard panic attack response card
03
iOS Harm Reduction

SafeGuard

Harm reduction toolkit with 84 response cards covering overdose, de-escalation, first aid, and mental health crises. Clear guidance when it matters.

SharePanel Support landing page
04
AI-Powered Support

SharePanel Support

AI-powered support system with automated resolution, smart routing via Gemini API, and role-based dashboards serving the entire SharePanel ecosystem.

MyADHD landing page
MyADHD login screen
05
iOS Neurodivergence

MyADHD

Energy-based task manager for ADHD minds. No guilt, no overdue warnings. Calm structure that works with your brain instead of yelling at it.

Cloud SaaS Architecture

SharePanel Host

Cloud hosting platform powering 2,400+ sites. Multi-tenant architecture, automated provisioning, integrated webmail, SSL management, six first-party integrations. Built from bare metal to UI.

Live chat, analytics, forms, auth, scheduling, CMS. All built in, zero third-party dependencies.

2.4k+sites deployed
180kchat messages
99.9%uptime
<50msavg response
sharepanel.host
SharePanel Host landing page
sharepanel.host/dashboard
SharePanel admin dashboard
06
MTA community feed
07
Social Platform

MTA SharePanel

University social network with real-time messaging, events, groups, and file sharing.

08
macOS Claude Private by design

Wicker

Every thread of your life, woven together. A native macOS app that gathers your work, correspondence, calendar, people and security into one calm place, with Claude as the mind that reads it all.

A written morning briefing, an inbox you can reply from, a living map of your relationships, a work board Claude curates. Everything stays on your Mac.

  • The vault, your database and your secrets never leave the Mac.
  • Claude Code sessions or the Claude API, picked in Settings.
  • SwiftUI on macOS 14+, a unit-tested Swift engine underneath.
bugrater.com

Where to hunt tonightOct 2026

  1. 1Flutter UK&I↑ +24%busy
  2. 2Klarna↑ +22%under-hunted
  3. 3Stripe↑ +20%under-hunted
  4. 4Instacart↑ +19%busy
  5. 5KAYAK↑ +16%under-hunted
153programs rated
16,133credit lines
4,716researchers
09
Security Ratings & Reviews

BugRater

Independent ratings and researcher reviews of bug bounty programs: triage speed, payout fairness, communication, and whether researchers would submit again.

Security research

Independent vulnerability research across major vendors. Findings confirmed by engineering teams, CVEs published, patches merged.

Apple
Acknowledged in the iOS 27, tvOS 27, watchOS 27 and visionOS 27 security notes for two bluetoothd memory-corruption bugs.
Microsoft
CVE-2026-69446. Edge and To Do for macOS: DYLD injection to root and to OAuth token theft.
MongoDB
Compass: one click from a database name to code execution. Reported through HackerOne.
Zen Browser
CVE-2026-41431. Signature verification bypass. GHSA accepted, patches merged upstream.
Open WebUI
CVE-2026-59224. A terminal proxy that forwards spoofable identity upstream.
HackerOne
Coordinated disclosure through bug bounty programs, including MongoDB and Nord Security.

Reverse Engineering

Binary analysis with Ghidra and LLDB. XPC protocol reversing, daemon auditing, sandbox policy analysis on macOS.

Exploit Development

Proof-of-concept development targeting privilege escalation, symlink races, info disclosure, auth bypass.

Responsible Disclosure

Reports across multiple vendors. Findings reproduced by engineering teams. Clean disclosure process maintained throughout.

Thinking out loud

Research, analysis, and personal essays outside the technical work.

“
You cannot shoot down a narrative. A missile has a return address. A disinformation campaign shared by thousands of unwitting citizens does not.
Disinformation as the Single Greatest Threat to Canadian Security
POLS 1001B — Foundations of Politics · 9 pages · 13 sources · Winter 2026
FARPSEC · Security Advisory
CVE-2026-41431 · GHSA-qpj9-m8jc-mw6q
Zen Browser MAR Updater Ships with Signature Verification Removed
The auto-update mechanism accepted unsigned MAR files. No cryptographic verification, no signing keys, no channel enforcement. A compromised update server could push arbitrary code to every installation. Structural proof across 4 independent layers. GHSA accepted, patches merged upstream.
4-layer proof Patched GHSA accepted

Through the North

Landscapes and sunsets from a road trip across western Canada. BC to the Northwest Territories.

Crimson mackerel sky over marina
Crimson mackerel sky
Surfer entering misty Pacific
Into the Mist
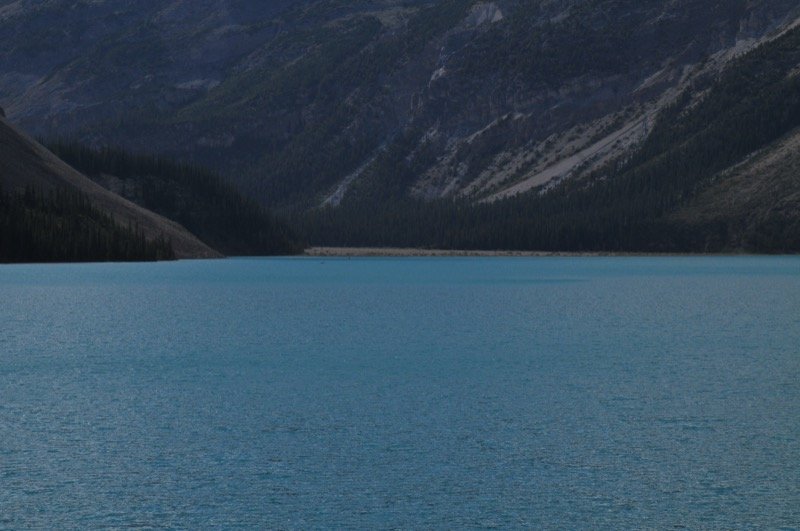
Turquoise alpine lake
Emerald Waters
Suspension bridge in rainforest
Suspension
Waterfall into teal coastal inlet
Hidden Falls
Maliq Barnard

Three years building systems.
Now I build the ones that break things.

Third-year university student with three years of self-taught development behind me. Production hosting platforms, university-scale social networks, automation pipelines. Real systems serving real users.

The building never stopped; it turned around. The systems I build now are the ones that break things: analysis pipelines that trace interfaces from version to version, an autonomous app-security harness, attack-surface mappers and recon tools. Knowing how production systems are put together is what tells them where to look.

Build Stack
  • Python / PHP / JavaScript
  • Swift / SwiftUI
  • React / Node.js
  • Linux / Docker / Nginx
  • MySQL / SQLite / PostgreSQL
Break Stack
  • LLDB / Ghidra
  • XPC / NSXPC Reversing
  • macOS Internals
  • Binary Analysis / Fuzzing

Let's talk.

Available for development work, system architecture, or security consultation.

Location
Canada, AST/ADT
Send a message
○ △ △ △ ▲ △ ▲ ▲ ● △